SFTP USER + ROLE + HOME DIRECTORY
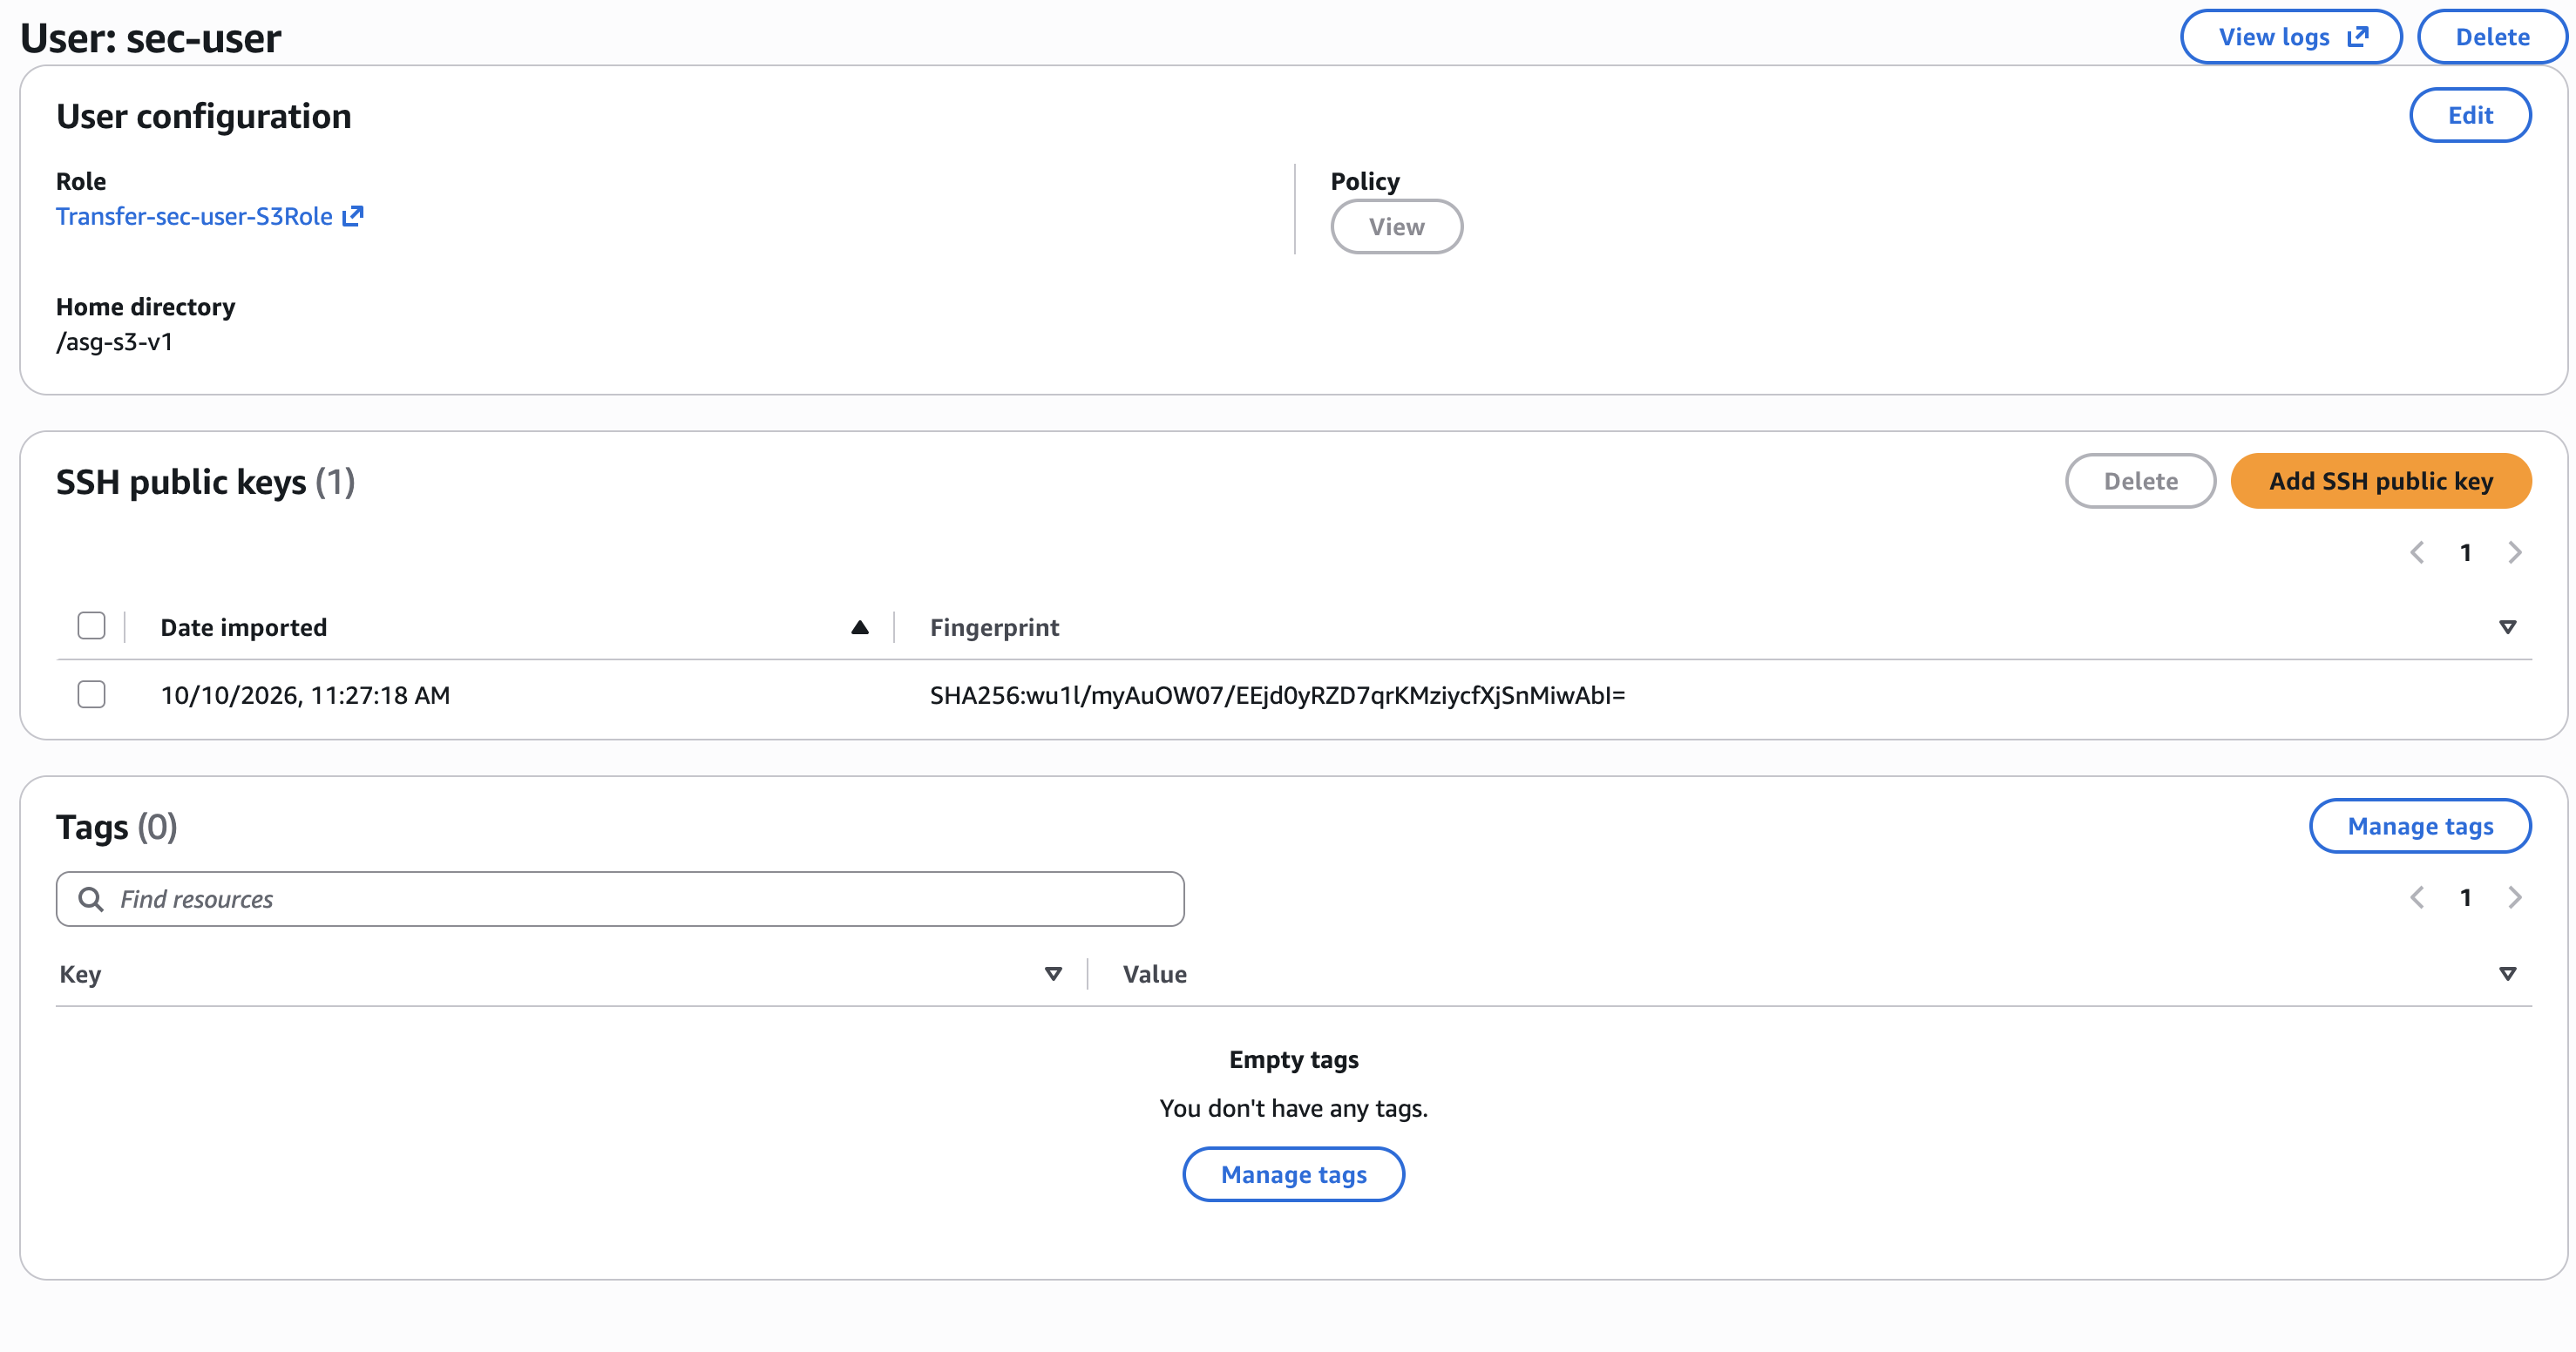
SFTP User configuration set with a role and home directory
We assign an IAM role to the user that allows AWS Transfer Family to access the assigned S3 bucket and prefix. We also configure the SFTP user’s home directory so that, after login, the session opens at the intended location on the SFTP server.
AWS TRANSFER SFTP SERVER NOW HAS ACCESS TO S3
The user can only access a specific folder within the bucket—the S3 prefix
The role can perform s3:GetBucketLocation, s3:ListBucket, and s3:ListBucketMultipartUploads on the bucket, scoped by a condition for the specified prefix. All S3 object actions are allowed only within that specific folder in the bucket.
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "ViewBucketAndListUserPrefix",
      "Effect": "Allow",
      "Action": [
        "s3:GetBucketLocation",
        "s3:ListBucket",
        "s3:ListBucketMultipartUploads"
      ],
      "Resource": "arn:aws:s3:::example-transfer-bucket",
      "Condition": {
        "StringLike": {
          "s3:prefix": [
            "restricted-user",
            "restricted-user/",
            "restricted-user/*"
          ]
        }
      }
    },
    {
      "Sid": "AllObjectOperationsInsideUserPrefix",
      "Effect": "Allow",
      "Action": "s3:*",
      "Resource": [
        "arn:aws:s3:::example-transfer-bucket/restricted-user",
        "arn:aws:s3:::example-transfer-bucket/restricted-user/*"
      ]
    }
  ]
}TRUST POLICY
Let only this Transfer server assume the role
We need to trust the AWS Transfer service to use this role.
{
  "Version": "2012-10-17",
  "Statement": [{
    "Effect": "Allow",
    "Principal": { "Service": "transfer.amazonaws.com" },
    "Action": "sts:AssumeRole",
    "Condition": {
      "StringEquals": {
        "aws:SourceAccount": "123456789012"
      },
      "ArnLike": {
        "aws:SourceArn": "arn:aws:transfer:us-east-1:123456789012:user/s-0123456789abcdef0/*"
      }
    }
  }]
}TESTING........
sftp -i transfer-key restricted-user@s-0123456789abcdef0.server.transfer.us-east-1.amazonaws.com
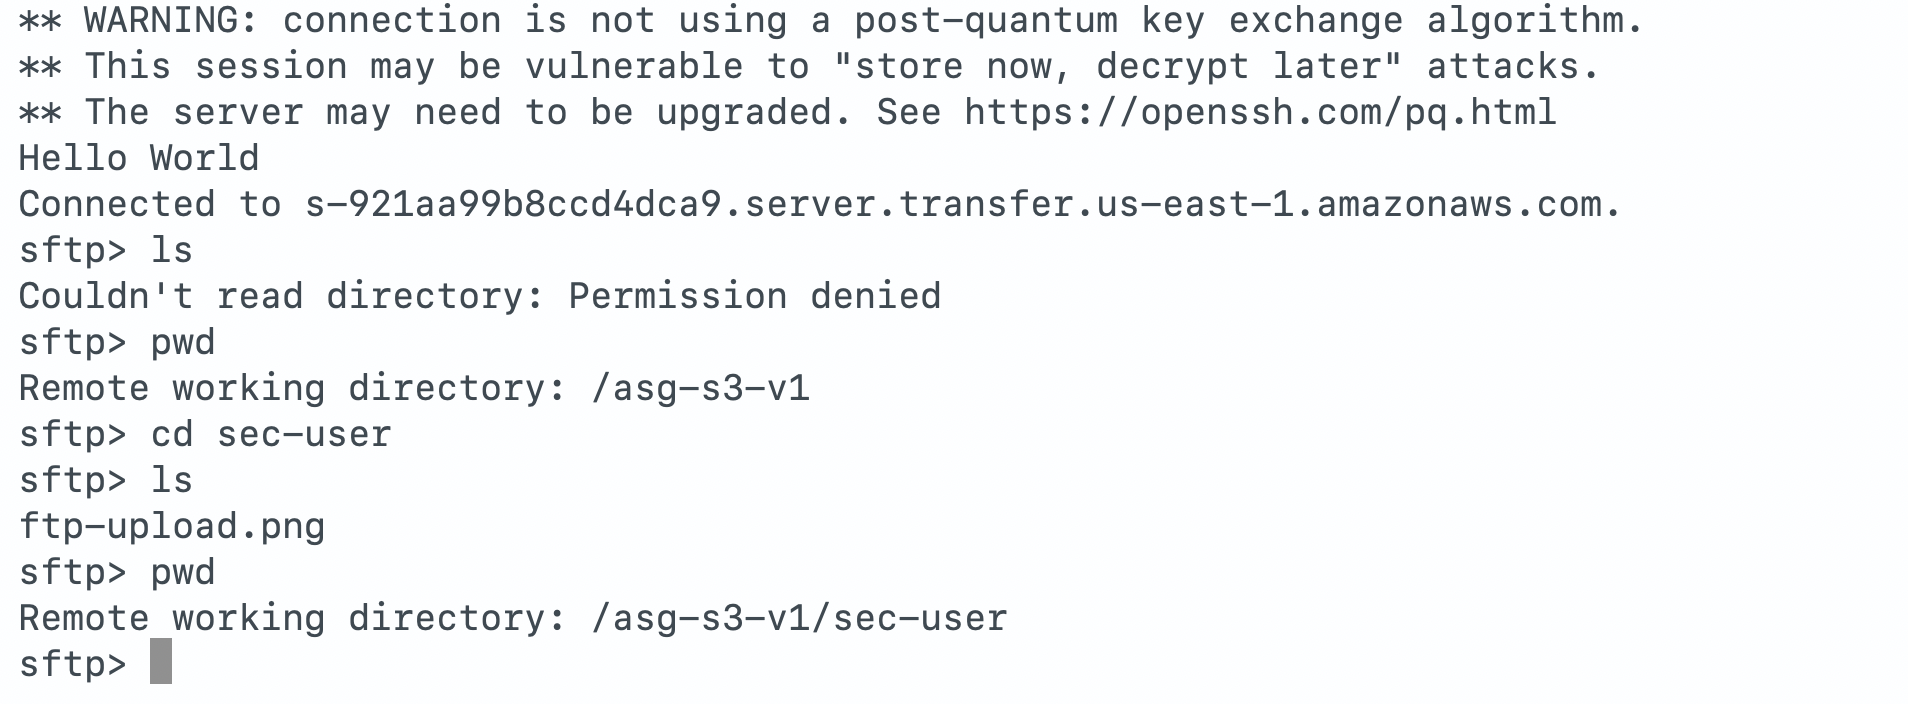
We log in to the SFTP server and find that the current directory cannot be listed because the role grants access only to the restricted-user folder within the bucket. After changing into restricted-user, we can run ls and see the files in the allowed directory.
SPRINKLE WITH S3 BUCKET POLICY
Role + Bucket Policy
The bucket policy allows the role to get the bucket location, list objects matching the chosen S3 prefix, and perform object operations only inside that prefix.
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "AllowTransferUserBucketLocation",
      "Effect": "Allow",
      "Principal": {
        "AWS": "arn:aws:iam::123456789012:role/Transfer-restricted-user-S3Role"
      },
      "Action": "s3:GetBucketLocation",
      "Resource": "arn:aws:s3:::example-transfer-bucket"
    },
    {
      "Sid": "AllowTransferUserListPrefix",
      "Effect": "Allow",
      "Principal": {
        "AWS": "arn:aws:iam::123456789012:role/Transfer-restricted-user-S3Role"
      },
      "Action": "s3:ListBucket",
      "Resource": "arn:aws:s3:::example-transfer-bucket",
      "Condition": {
        "StringLike": {
          "s3:prefix": [
            "restricted-user",
            "restricted-user/",
            "restricted-user/*"
          ]
        }
      }
    },
    {
      "Sid": "AllowTransferUserObjectOperations",
      "Effect": "Allow",
      "Principal": {
        "AWS": "arn:aws:iam::123456789012:role/Transfer-restricted-user-S3Role"
      },
      "Action": "s3:*",
      "Resource": [
        "arn:aws:s3:::example-transfer-bucket/restricted-user",
        "arn:aws:s3:::example-transfer-bucket/restricted-user/*"
      ]
    }
  ]
}AWS DOCUMENTATION